
Blog
Cloud security lessons, Zero Trust insights, and the occasional cat joke.
New Pods, Same Finding: Testing Defender’s Kubernetes Controller Scope

On October 5, 2026, Microsoft announced a welcome change to how Microsoft Defender for Cloud reports Kubernetes misconfigurations. Affected Kubernetes Security Posture Management (KSPM) recommendations are moving from individual running container …
Microsoft Security Fall 2026: Five Changes to Prepare For

Review update (September 25, 2026): The integration identity used for incident comments can require tenant-wide incident-write permission, not a comment-only grant. Keep a dedicated identity, narrowly selected integrations and documented credential …
Entra SSPR and Passkey Readiness for Microsoft-Provided SMS/Voice Delivery Retirement

Microsoft is advancing three related parts of the Entra authentication and recovery experience through July 2027: On September 1, 2026, Microsoft began gradually moving users enabled for SMS or voice into the Microsoft-managed passkey Registration …
GigaWiper Detection as Code: Testing Custom Detections in Sentinel Repositories
Review update (September 25, 2026): The merged September 25 source now chooses a labeled executable identity from populated SHA1, then SHA256, then a normalized path; it excludes empty identity values. Its KQL semantic analysis and offline suite …
From Authorization to Action: Operationalizing CISA's Microsoft Cloud Logs Playbook in Sentinel
Review update (September 25, 2026): The January 15, 2025 publication date is supported by CISA’s original release notice; the resource landing page now emphasizes the later revision date. Review update (September 25, 2026): For cost planning, …
Copy Fail in the Cloud: A Defender, Sentinel, and AKS Response Guide for CVE-2026-31431
Review update (September 25, 2026): The retained Sentinel/AKS evidence was captured May 2, 2026, without executing Copy Fail exploit code. The May 3 CVE/KEV snapshot remains historical; its May 15 due date has passed. Recheck the live NVD record and …
Block Device Code Phishing in Entra Without Breaking Legit Workflows
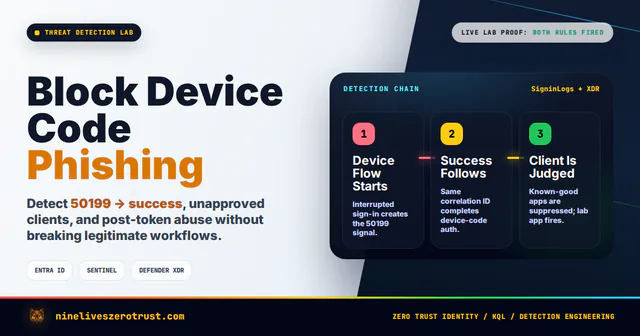
Review update (September 26, 2026): The merged rules run every 15 minutes, retain their correlation lookbacks, and gate on recent ingestion from either relevant side. Rule 2 merges duplicate representations of a successful sign-in while retaining …
Agent 365 Launch Playbook: I Tested the Defender Response for AI Agent Attacks
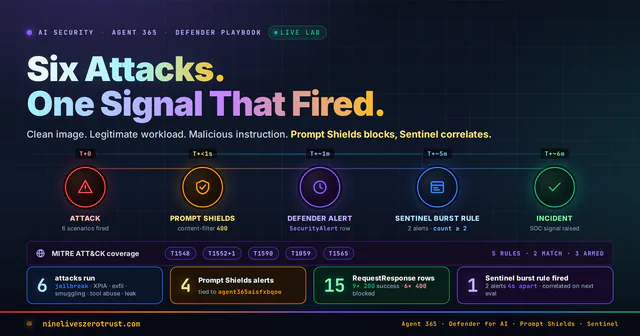
Review update (September 26, 2026): The source reviewed September 26 requires explicit GA model/version selection and Python 3.12 hash-locked dependencies. Current rules use stable alert IDs and ingestion freshness, without a fixed artificial …
Scan Blob Uploads, Trace Later Reads: Defender for Storage + Sentinel
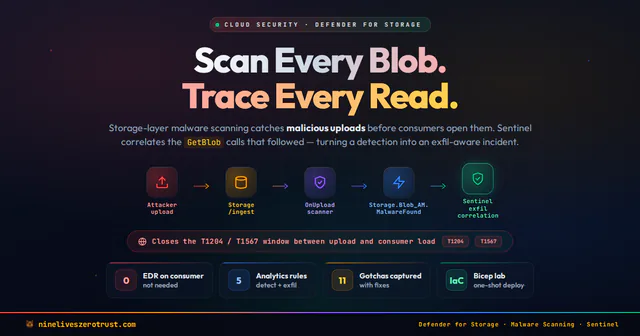
Review update (September 25, 2026): The merged source disables Shared Key, uses the stable 2025-06-01 account settings API, scopes every StorageBlobLogs workbook panel to the lab account, and shows four correctly defined KPI tiles. It passed 35 …
Detecting Infostealer Session Hijacking with Microsoft Sentinel
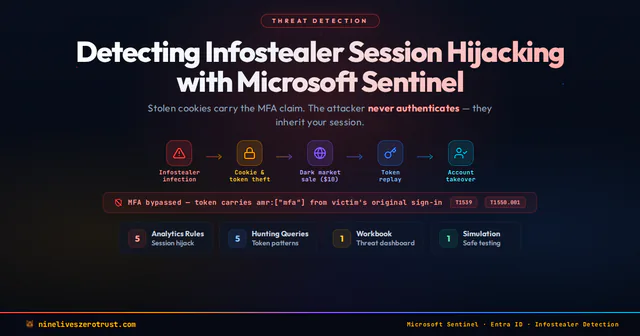
Review update (September 25, 2026): Cookie replay maps to T1550.004 separately from cookie theft (T1539); these rules provide investigative signals rather than proof of either technique. Keep the sign-in tables used by scheduled rules in the …