
Detection Engineering
Lessons from the field. Always landing on my feet.
GigaWiper Detection as Code: Testing Custom Detections in Sentinel Repositories
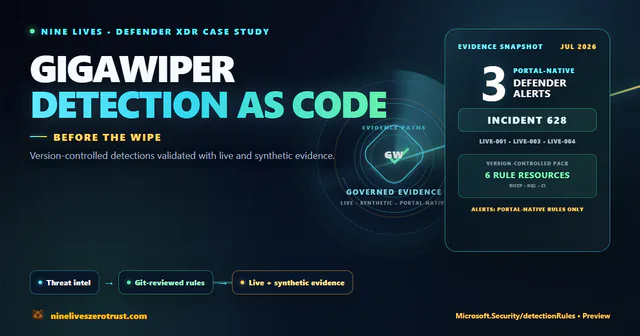
Review update (September 25, 2026): The merged September 25 source now chooses a labeled executable identity from populated SHA1, then SHA256, then a normalized path; it excludes empty identity values. Its KQL semantic analysis and offline suite …
From Authorization to Action: Operationalizing CISA's Microsoft Cloud Logs Playbook in Sentinel
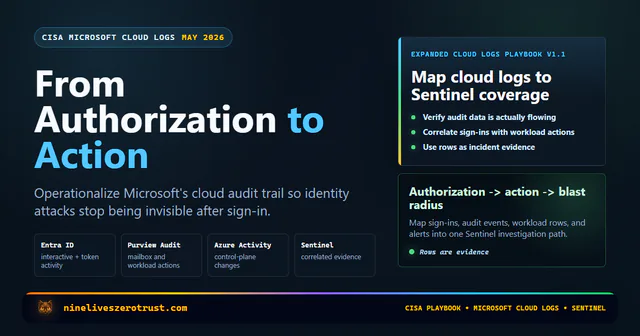
Review update (September 25, 2026): The January 15, 2025 publication date is supported by CISA’s original release notice; the resource landing page now emphasizes the later revision date. Review update (September 25, 2026): For cost planning, …
Detecting Infostealer Session Hijacking with Microsoft Sentinel
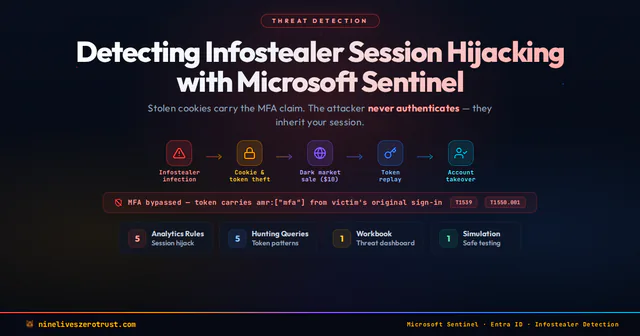
Review update (September 25, 2026): Cookie replay maps to T1550.004 separately from cookie theft (T1539); these rules provide investigative signals rather than proof of either technique. Keep the sign-in tables used by scheduled rules in the …
Investigate Hidden Privilege Paths with Microsoft Sentinel Data Federation and Custom Graphs
Review update (September 25, 2026): Modeling, persistence and query permissions differ. Review the current graph requirements before granting tenant-wide Security Operator or Administrator solely to persist a graph. An on-demand graph job and a …
Building Custom Sentinel Connectors with CCF Push
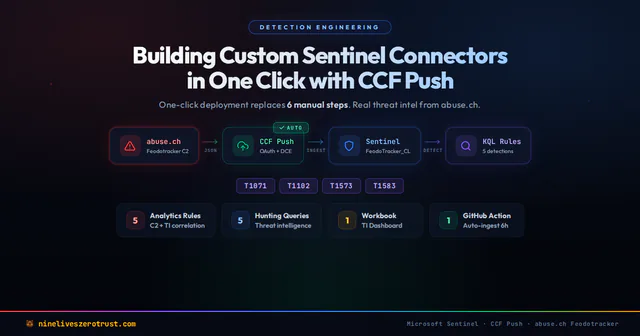
Review update (September 25, 2026): The repaired sender treats a genuine empty upstream list as a successful zero-record poll without authentication or ingestion; a nonempty all-invalid list still fails. Rule enablement is a second phase after …
The February 2026 Microsoft Sentinel Drop: UEBA Essentials, Copilot Connector, and 9 New GA Connectors
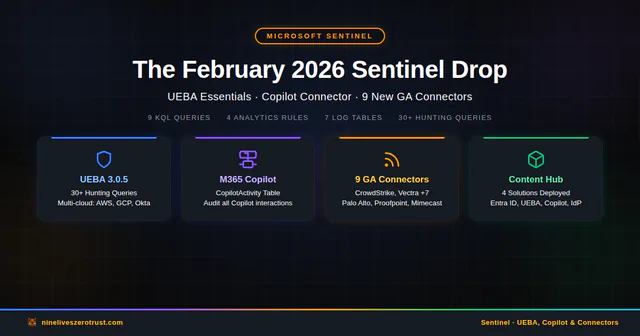
Review update (September 25, 2026): The diagram and measured results describe February evidence. For current use, Defender-portal onboarding replaces Fusion incident correlation with the Defender XDR engine. Connector descriptions refer to what is …