
detection-engineering
Lessons from the field. Always landing on my feet.
Detecting Infostealer Session Hijacking with Microsoft Sentinel
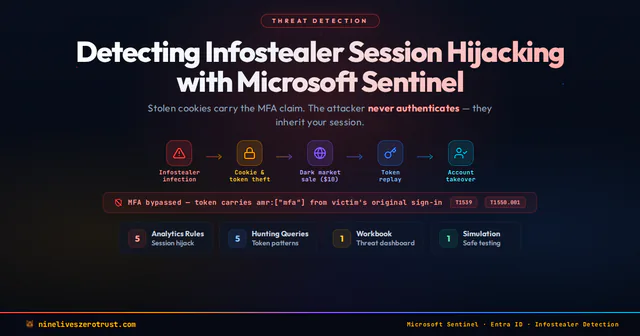
Review update (September 25, 2026): Cookie replay maps to T1550.004 separately from cookie theft (T1539); these rules provide investigative signals rather than proof of either technique. Keep the sign-in tables used by scheduled rules in the …
Building Custom Sentinel Connectors with CCF Push
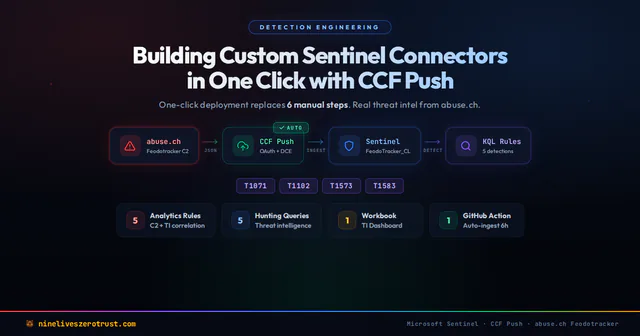
Review update (September 25, 2026): The repaired sender treats a genuine empty upstream list as a successful zero-record poll without authentication or ingestion; a nonempty all-invalid list still fails. Rule enablement is a second phase after …
Detecting OAuth Redirect Abuse with Microsoft Sentinel and Entra ID
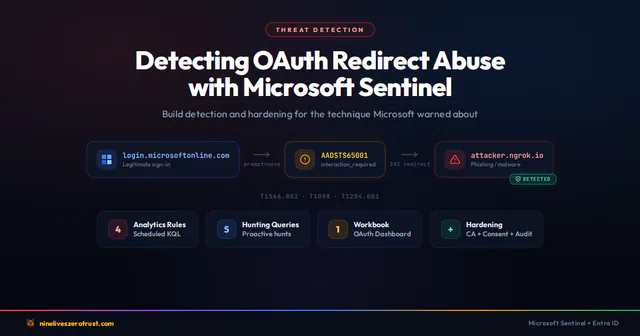
Review update (September 26, 2026): The merged source preserves an already-disabled user-consent policy and refuses unrecognized custom self-consent policy replacement for manual review. Reports, manifest staging and request-body files are …