
microsoft-defender
Lessons from the field. Always landing on my feet.
Microsoft Security Fall 2026: Five Changes to Prepare For

Review update (September 25, 2026): The integration identity used for incident comments can require tenant-wide incident-write permission, not a comment-only grant. Keep a dedicated identity, narrowly selected integrations and documented credential …
GigaWiper Detection as Code: Testing Custom Detections in Sentinel Repositories
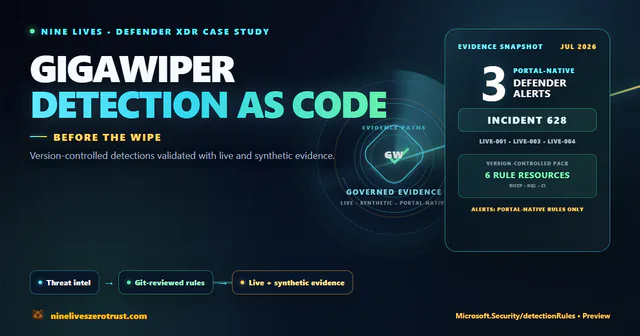
Review update (September 25, 2026): The merged September 25 source now chooses a labeled executable identity from populated SHA1, then SHA256, then a normalized path; it excludes empty identity values. Its KQL semantic analysis and offline suite …
Copy Fail in the Cloud: A Defender, Sentinel, and AKS Response Guide for CVE-2026-31431
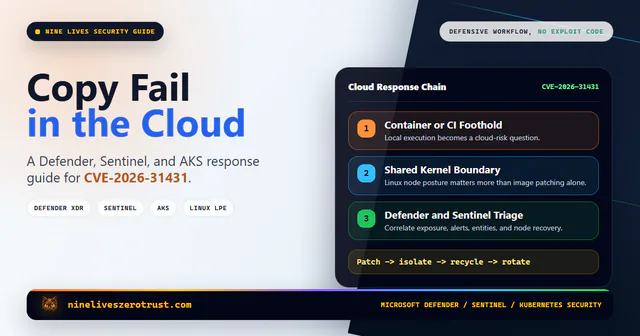
Review update (September 25, 2026): The retained Sentinel/AKS evidence was captured May 2, 2026, without executing Copy Fail exploit code. The May 3 CVE/KEV snapshot remains historical; its May 15 due date has passed. Recheck the live NVD record and …
Block Device Code Phishing in Entra Without Breaking Legit Workflows
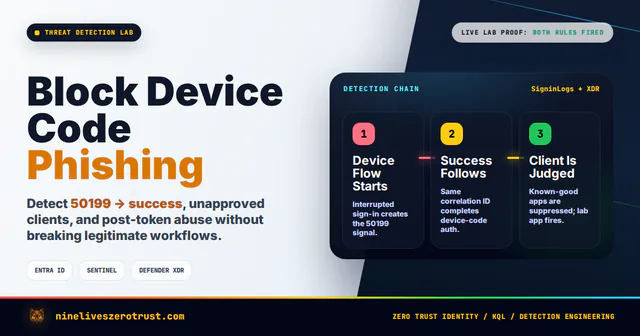
Review update (September 26, 2026): The merged rules run every 15 minutes, retain their correlation lookbacks, and gate on recent ingestion from either relevant side. Rule 2 merges duplicate representations of a successful sign-in while retaining …