
mitre-attack
Lessons from the field. Always landing on my feet.
GigaWiper Detection as Code: Testing Custom Detections in Sentinel Repositories
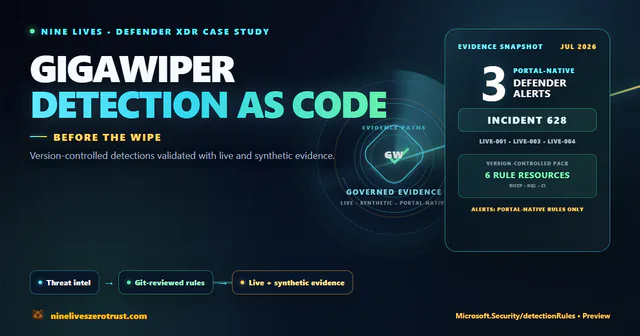
Review update (September 25, 2026): The merged September 25 source now chooses a labeled executable identity from populated SHA1, then SHA256, then a normalized path; it excludes empty identity values. Its KQL semantic analysis and offline suite …
Scan Blob Uploads, Trace Later Reads: Defender for Storage + Sentinel
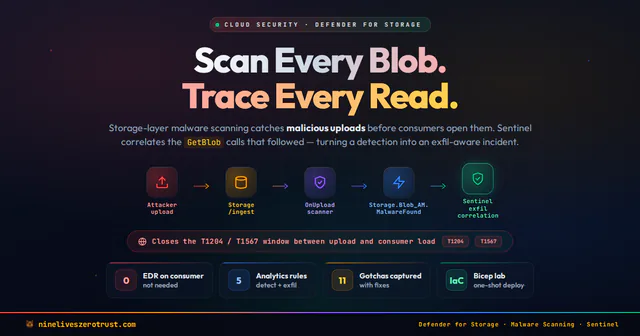
Review update (September 25, 2026): The merged source disables Shared Key, uses the stable 2025-06-01 account settings API, scopes every StorageBlobLogs workbook panel to the lab account, and shows four correctly defined KPI tiles. It passed 35 …
Detecting Infostealer Session Hijacking with Microsoft Sentinel
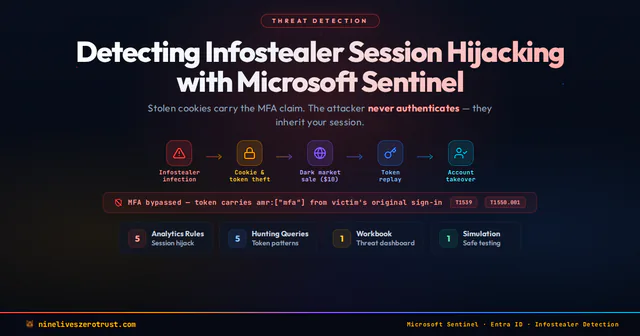
Review update (September 25, 2026): Cookie replay maps to T1550.004 separately from cookie theft (T1539); these rules provide investigative signals rather than proof of either technique. Keep the sign-in tables used by scheduled rules in the …
Building Custom Sentinel Connectors with CCF Push
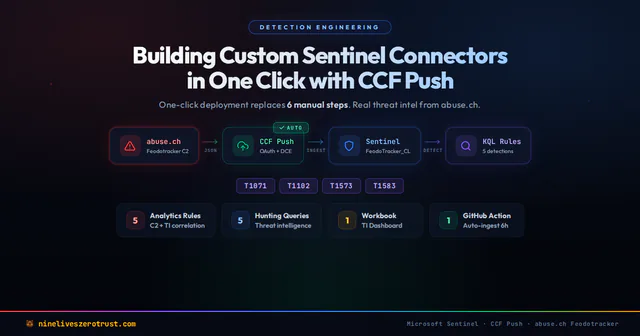
Review update (September 25, 2026): The repaired sender treats a genuine empty upstream list as a successful zero-record poll without authentication or ingestion; a nonempty all-invalid list still fails. Rule enablement is a second phase after …
AKS Runtime Security: Binary Drift, Anti-Malware & Gated Deployment with Defender for Cloud
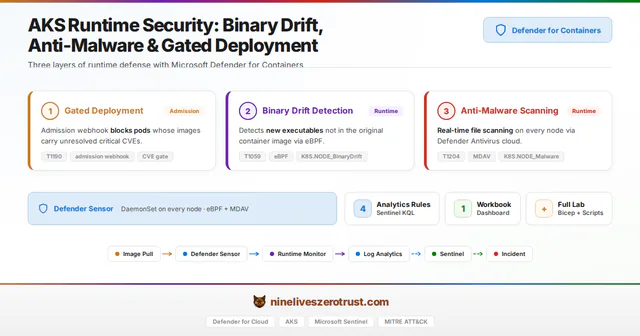
Review update (September 25, 2026): The merged September 25 source resolves and records an exact regional GA Kubernetes patch on first deployment and refuses implicit version changes on owned reruns. Pricing restoration is bound to the captured …
Detecting OAuth Redirect Abuse with Microsoft Sentinel and Entra ID
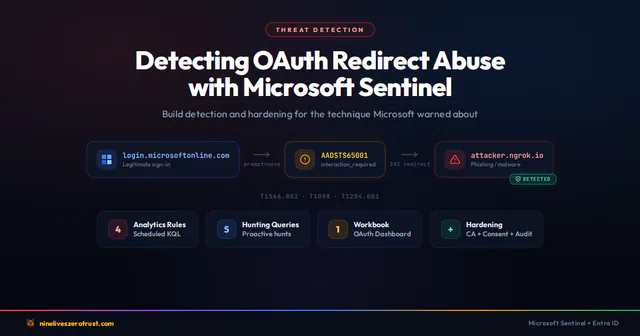
Review update (September 26, 2026): The merged source preserves an already-disabled user-consent policy and refuses unrecognized custom self-consent policy replacement for manual review. Reports, manifest staging and request-body files are …