
oauth
Lessons from the field. Always landing on my feet.
All
Cloud Security
Identity Security
Microsoft Sentinel
Microsoft Defender
AI Security
Detection Engineering
Threat Detection
Container Security
Entra ID
Zero Trust
DevSecOps
Infrastructure as Code
Agentic AI
2 posts
Block Device Code Phishing in Entra Without Breaking Legit Workflows
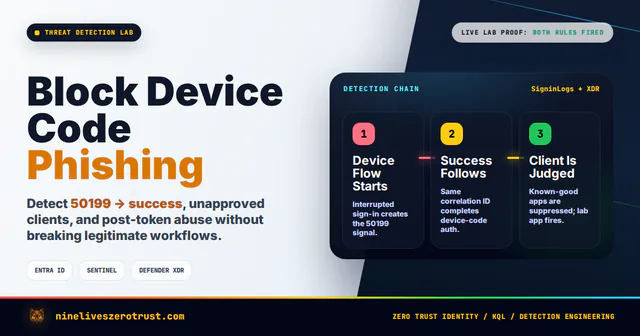
Review update (September 26, 2026): The merged rules run every 15 minutes, retain their correlation lookbacks, and gate on recent ingestion from either relevant side. Rule 2 merges duplicate representations of a successful sign-in while retaining …
Detecting OAuth Redirect Abuse with Microsoft Sentinel and Entra ID
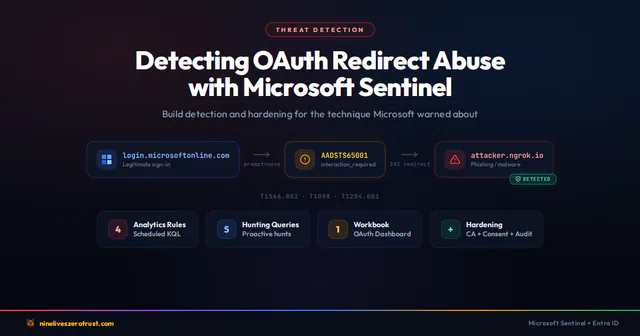
Review update (September 26, 2026): The merged source preserves an already-disabled user-consent policy and refuses unrecognized custom self-consent policy replacement for manual review. Reports, manifest staging and request-body files are …