
token-theft
Lessons from the field. Always landing on my feet.
All
Cloud Security
Identity Security
Microsoft Sentinel
AI Security
Detection Engineering
Microsoft Defender
Threat Detection
Entra ID
Container Security
Zero Trust
DevSecOps
Infrastructure as Code
Agentic AI
2 posts
Block Device Code Phishing in Entra Without Breaking Legit Workflows
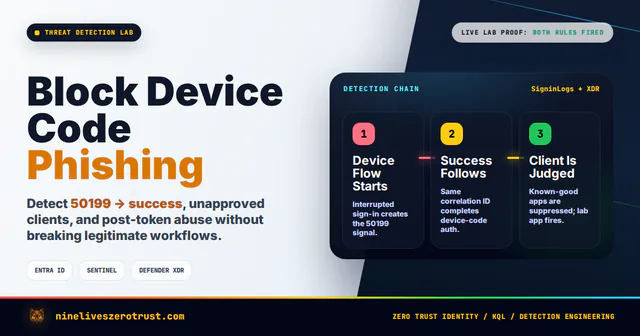
Review update (September 26, 2026): The merged rules run every 15 minutes, retain their correlation lookbacks, and gate on recent ingestion from either relevant side. Rule 2 merges duplicate representations of a successful sign-in while retaining …
Detecting Infostealer Session Hijacking with Microsoft Sentinel
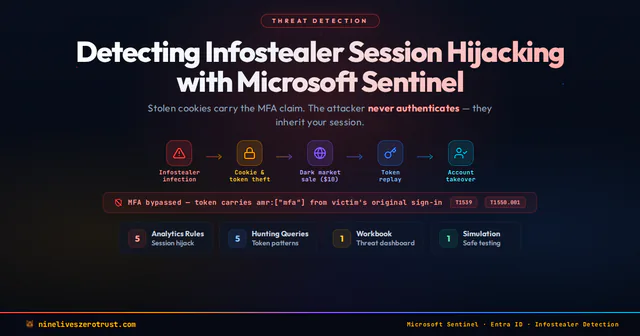
Review update (September 25, 2026): Cookie replay maps to T1550.004 separately from cookie theft (T1539); these rules provide investigative signals rather than proof of either technique. Keep the sign-in tables used by scheduled rules in the …